

SSL Certificates
The SSL Certificates page lists every certificate AdminBolt knows about, and records every attempt to issue one. Open it from SSL > Certificates in the sidebar.
Overview
URL: /admin/certificates
The page has three tabs:
- Certificates - the certificates currently installed, with their owner, type, and expiry.
- Issuance History - every issuance attempt, successful or not, with the reason a failed attempt failed. See SSL Issuance History.
- AutoSSL - AutoSSL switched on or off per hosting account and, since panel 1.9.2, how far AutoSSL has got. See SSL for hosting accounts and AutoSSL progress.
The Certificates entry in the sidebar carries a counter showing how many certificates are installed.
The certificate list
Each row shows:
- Domain - the main domain the certificate is issued for. Non-ASCII domain names are listed in their readable Unicode form; the certificate itself is issued for the Punycode name. See Internationalised domain names.
- Owner - the hosting account that owns the certificate (sortable).
- Type - the issuing provider, for example Let's Encrypt or ZeroSSL (sortable).
- Expiration - the expiry date (sortable).
The Type filter narrows the list down. Since panel 1.9.3 it is a filter of the table rather than a second row of tabs:
| Filter value | What it shows |
|---|---|
| Free SSL | Certificates from free providers such as Let's Encrypt and ZeroSSL. |
| Private SSL | Certificates you bought elsewhere and imported. |
| Self-Signed | Self-signed certificates, including the one the panel generates for itself. |
With no value chosen, the list shows every certificate.
A search box filters the list by domain.
How issuance works
Issuing a certificate is an asynchronous operation. When you or an automatic policy asks for a certificate, AdminBolt hands the work to Bolt Agent on the server and the page keeps polling until the operation finishes. You can leave the page while it runs.
Before the request goes out, AdminBolt checks public DNS for the domain. A name that does not resolve to this server cannot pass the certificate authority's own check, so the attempt is stopped early and recorded with that reason instead of failing several minutes later.
Every attempt, whether it succeeds or not, lands in Issuance History.
Note: Certificate authorities validate the domain over HTTP. The domain must resolve publicly to this server, and the server must answer on port 80, before an attempt can succeed.
AutoSSL on servers with many domains
Since panel 1.9.2, AutoSSL keeps going on a server with thousands of domains, for example after many accounts were moved in at once:
- One run at a time. The nightly run, the hourly check for new domains, and the run for a newly added domain take turns. A domain whose own run finds another run in progress is queued for that run or the next one, not dropped.
- No stalls on one order. AutoSSL works on several orders at once, so a slow order holds up only its own domain. Something that goes wrong before or during one domain's order fails that domain only, and the run goes on with the rest. Domains whose orders failed recently are ordered after the others, so they do not take the first places of every run.
- Within the certificate authority's limits. AutoSSL counts the orders placed with each authority, its own and those placed from the panel, against the authority's rate limit, where it has one. When the limit is reached, or the authority refuses new orders on its rate limit, the run leaves the remaining domains for a later run. That run starts by itself once the authority accepts orders again, renewals included, so you do not need to start it.
- Not while Apache is stopped. A domain is validated over HTTP, so while Apache is not running, AutoSSL places no orders and leaves the domains for a later run, which starts once the web server serves again.
A certificate ordered by hand while the authority's limit is reached is refused with "Too many certificates were ordered in a short time. Try again after time UTC.", and nothing needs changing: order it again once the limit has passed.
AutoSSL progress
The AutoSSL tab shows an AutoSSL progress section above the accounts, which refreshes on its own:
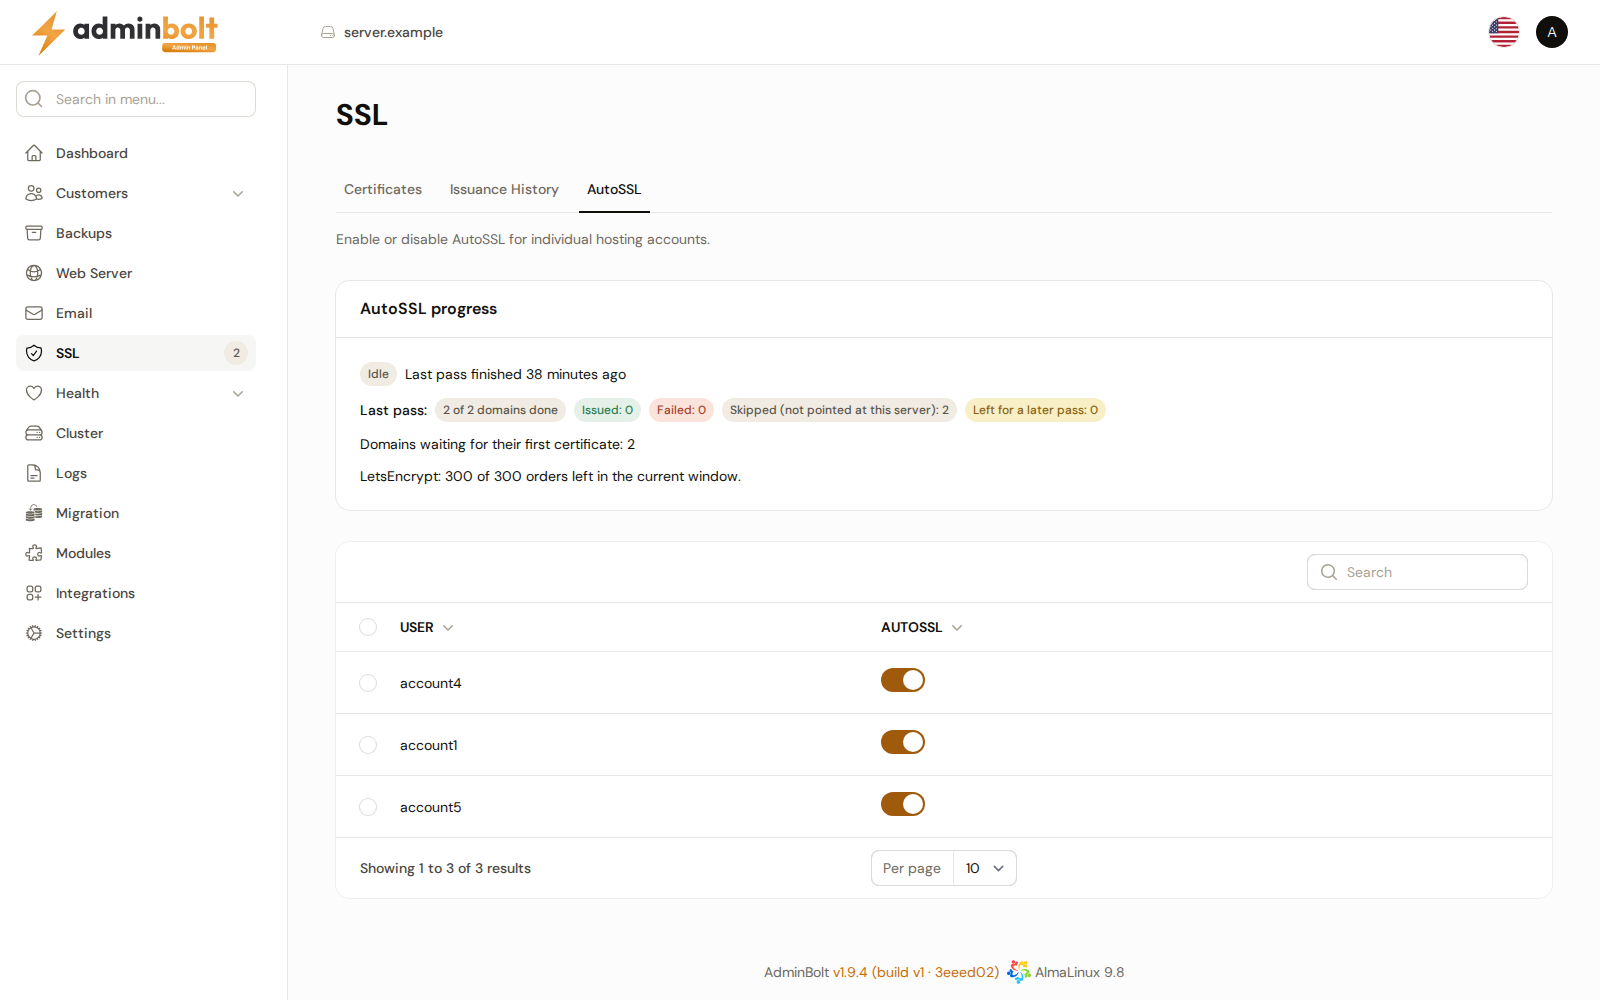
| Shown | Meaning |
|---|---|
| Running, with when it started | A run over every domain is in progress. |
| Running, with "Issuing certificates for newly added domains" and the domain it is on | A run for newly added domains is in progress. The counts below are then those of the last full run. |
| Idle, with when the last run finished | Nothing is running. |
| Stopped | The last run stopped before it finished. The next one takes up the rest. |
Under the state come the counts of the current or the last run: how many domains are done out of how many it took up, for example 120 of 3500 domains done, then Issued, Failed, Skipped (not pointed at this server), and Left for a later pass. When domains were left, the section says from when they are taken up automatically.
The section also shows how many domains are still waiting for their first certificate and, for each certificate authority, how many orders are left in its current window and when the next order is possible, or until when the authority refused new orders. Times are in UTC.
From the command line, bolt-cli run-auto-ssl ends with the same counts. See Security commands.
Managing certificates
This page is an inventory: it shows what is installed. Each row has these actions:
- View - opens the page of that certificate, with its Domain, Owner, Type, and Expiration. Since panel 1.9.1.
- Replace with a free certificate - since panel 1.9.3, on a certificate that is not from a free provider. See Replacing a certificate with a free one.
- Issuance history - opens that domain's attempts.
Certificates are managed where they are used:
- Automatic issuance runs from the policy under Settings > SSL > SSL Providers, and every attempt is recorded in Issuance History.
- Importing or replacing a certificate by hand happens per domain, on the account's SSL Certificates screen in the client area. Paste the certificate, the private key, and optionally the chain there, and the imported certificate appears in this inventory. Since panel 1.9.1, an imported certificate is stored with automatic renewal off, so AutoSSL does not renew or replace it.
To list every domain whose certificate AutoSSL does not renew, and why, run bolt-cli run-auto-ssl --list-unmanaged. See Security commands.
Certificates that are not renewed automatically
AutoSSL renews the free certificates it manages. It never replaces a certificate from another issuer on its own, such as a certificate you imported, a certificate brought over from another server, or a self-signed one. A free certificate is not renewed either while AutoSSL is switched off for its hosting account or automatic renewal is off for the certificate. Such certificates have to be renewed with their issuer or replaced.
Expiry reminders
Since panel 1.9.3, every certificate that is not renewed automatically gets expiry reminders 30, 14, 7, and 1 days before it expires, and once it has expired. A certificate AutoSSL renews gets a reminder only shortly before it expires, in case the renewal does not happen.
- Administrators get the reminder in the notification bell, and by the channels set on System Notifications through the SSL certificate approaching its expiration date and SSL certificate has expired events. When many certificates reach a reminder at once, one summary replaces the single reminders.
- The account owner gets the reminder in the notification bell of the client panel, with a Replace with a free certificate button for a certificate that can be replaced. See SSL Certificates in the client panel. The owner's reminder follows the event that announces the certificate to administrators: SSL certificate approaching its expiration date or SSL certificate has expired for a single reminder, and Several SSL certificates approaching expiry in one scan or Several SSL certificates expired, reported in one scan when the certificate is part of a summary. Switching that event off on System Notifications also stops the owner's reminder.
A certificate without an expiry date, such as a self-signed one, gets no reminder.
Replacing a certificate with a free one
Since panel 1.9.3, Replace with a free certificate swaps a certificate from another issuer, an imported, private, or self-signed certificate, for a free one from the certificate provider set for the server. It is offered on the row of such a certificate, and in the header of its View page. It is not offered for a certificate that is already from Let's Encrypt or ZeroSSL.
- Click Replace with a free certificate on the certificate.
- Read the confirmation, "Replace the certificate for domain". It names the provider, and when AutoSSL is switched off for the hosting account, it warns that the free certificate will not be renewed automatically either: switch AutoSSL on for the account, or issue a new certificate before it expires.
- Click Replace certificate.
The installed certificate stays in place until the free one has been issued. If it cannot be issued, the notification gives the reason, and the current certificate keeps working. A domain that does not resolve to this server is refused before anything is ordered, and the attempt appears in Issuance History.
To replace several certificates, select them in the list and choose the bulk action Replace with free certificates, then Replace certificates. The certificates are replaced one after another in the background. Free certificates and certificates already being replaced are skipped, and the notification says how many were queued and skipped. When the certificate authority accepts no more orders for the moment, the rest are not started, and the notification says after what time to run the action again for them. When the run finishes, the notification bell gives the number replaced, failed, skipped, and not started, and names the failed domains.
In the administrator API
| Method and path | What it does |
|---|---|
POST /api/hosting-account/ssl-certificates/{domain_id}/replace-free | Replaces the certificate of one domain and answers when it is done. The request takes no body. It answers 409 when the domain has no certificate to replace. |
POST /api/hosting-account/ssl-certificates/replace-free-bulk | Queues the replacement of several certificates. The body takes domain_ids, a list of domain IDs. It answers 202 with how many were queued, skipped, already being replaced, and not started because of the certificate authority's limit, with the domain IDs of each group. |
The client API has the same two endpoints under /api/client/ssl-certificates. See the API reference.
SSL alerts in the notification bell
Since panel 1.9.1, SSL alerts, such as a certificate nearing its expiry date or an automatic renewal that failed, reach the notification bell of every administrator. An alert about one certificate has a View Certificate button that opens that certificate's page; since panel 1.9.3, for a certificate that can be replaced with a free one, the button reads Replace with a free certificate and opens the same page. An alert that covers several certificates has an SSL Certificates button that opens this list.
Certificates after a restore
A backup carries the account's certificates, so a restore can put back a certificate that is no longer valid. Since panel 1.9.1, after an in-place or whole-account restore, and after a JetBackup restore, an automatic certificate that the backup put back and that the panel has since replaced, or that has ended or been revoked, is issued again a few minutes after the restore.
- A certificate the customer uploaded stays as it is.
- For an account with AutoSSL switched off, no certificate is issued. The domain's Issuance history instead shows a failed attempt saying that the restored certificate may be revoked or expired and needs to be replaced. Issue a new certificate for the domain. See SSL Issuance History.
Where the related settings live
- Providers and the automatic issuance policy: Settings > SSL > SSL Providers (
/admin/settings/auto-ssl-providers). - Per account coverage: SSL for hosting accounts.
- The certificate for the server's own hostname, including a purchased one: General Settings, Hostname & SSL tab.